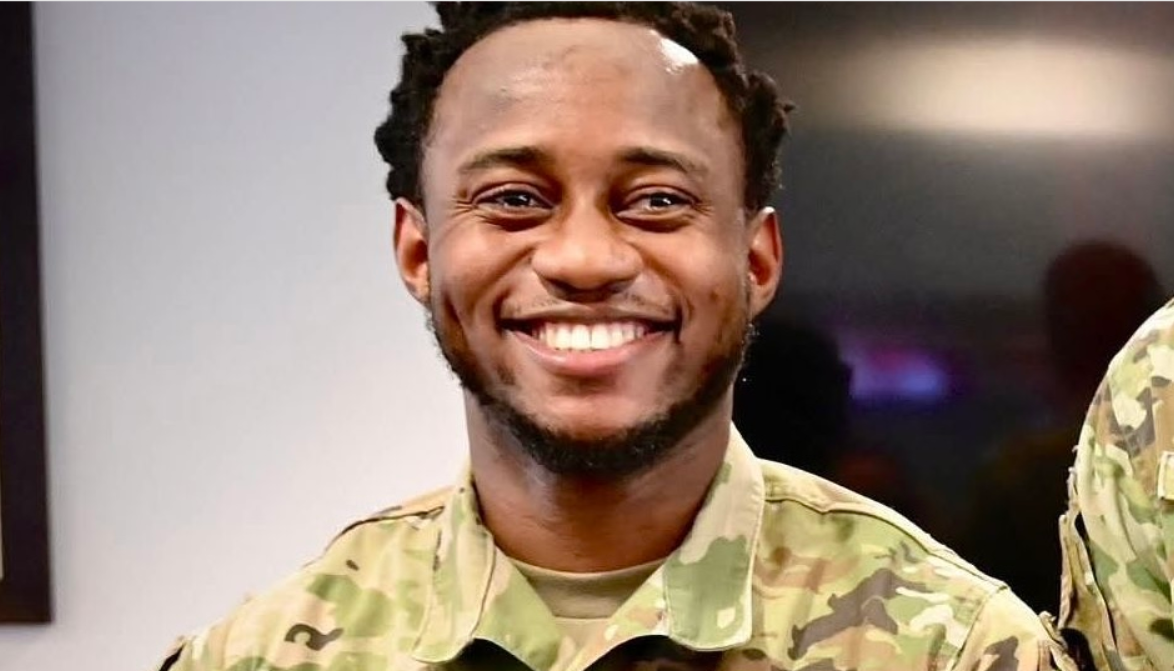
Two Nigerians serving in the United States Air Force have been sentenced to a combined 189 months in federal prison for their roles in an international cyber fraud scheme that targeted businesses and non-profit organizations across the country.
Chijioke Timothy Odimegwu, 25, received 111 months in prison, while Harafat Mogaji, 26, was sentenced to 78 months after prosecutors said they spent nearly two years using phishing and email-spamming campaigns to steal employee login credentials and divert legitimate business payments to accounts controlled by their network.
The sentences were handed down on September 25, 2026, in the US District Court for the Southern District of Iowa. Both men were residents of Delaware and were members of the US Air Force at the time of the offences, with court records and local reports indicating that they were stationed at Dover Air Force Base.
According to the US Department of Justice, the pair and their co-conspirators used phishing emails to obtain usernames and passwords for employees’ email accounts.
They then used the stolen credentials alongside spoofed email addresses designed to resemble those of businesses or their trusted partners.
The compromised accounts enabled the group to monitor communications involving payments and insert themselves into legitimate business transactions.
Fraudulent messages were then used to provide new payment instructions, redirecting funds intended for legitimate recipients into bank accounts controlled by members of the conspiracy.
One of the largest identified transactions involved more than $1.68 million sent by a victim in Iowa City. Prosecutors said the money was diverted to a Chicago bank account controlled by the conspiracy.
The group also diverted more than $720,000 from a victim in Ohio, while making several other attempts to redirect wire transfers involving businesses in Iowa and elsewhere in the United States.
Also Read: DOJ probes ex-Trump aide Hutchinson
The indictment identified at least 15 corporate, public-sector or non-profit organizations as victims or attempted victims.
The Ohio case involved the city of Athens, which lost about $721,976 in November 2024 while making a payment connected to the construction of a fire station.
The city later recovered $205,000 from funds that had been frozen and received another $200,000 through an insurance claim, according to local officials.
Beyond diverting wire transfers, prosecutors said Odimegwu and Mogaji harvested financial information from victims, including bank account details, personal identification numbers and credit and debit card information.
They also obtained additional stolen financial data from co-conspirators and used it to make or attempt unauthorized transactions and purchases.
The scheme is an example of business email compromise, BEC, a form of cyber-enabled fraud in which criminals compromise or impersonate legitimate business email accounts to deceive victims into transferring money or revealing sensitive information.
BEC remains a significant financial threat in the United States. The FBI recorded 24,768 BEC complaints involving more than $3 billion in reported losses in 2025, underscoring the scale of attacks involving fraudulent payment instructions and compromised business communications.
The investigation was led by the Federal Bureau of Investigation, with assistance from the US Air Force Office of Special Investigations. Prosecutors said the case involved co-conspirators both in the United States and abroad.
Following their sentencing, both men were taken into custody. Odimegwu was ordered to pay $366,617.59 in restitution, while Mogaji was ordered to pay $995,680.45.
Each will also serve three years of supervised release after completing the prison sentence. FBI Omaha Special Agent in Charge Eugene Kowel said the case demonstrated that cybercriminals targeting businesses and individuals would be pursued by law enforcement, stressing that digital systems ranging from corporate networks to personal devices remain vulnerable to cybercrime.
The case highlights how phishing, stolen credentials and convincing email impersonation can be combined to compromise otherwise legitimate financial transactions, turning routine business communications into a pathway for large-scale fraud.
DOJ